Cyberattack disrupts blood storage refrigeration systems in France
France's national blood service has confirmed that a cyberattack targeting a refrigeration equipment provider raised temperature and defrost settings at three of its facilities, threatening stored blood products. [...]
Cyberattack disrupts blood storage refrigeration systems in France
- November 4, 2026
- 01:02 PM
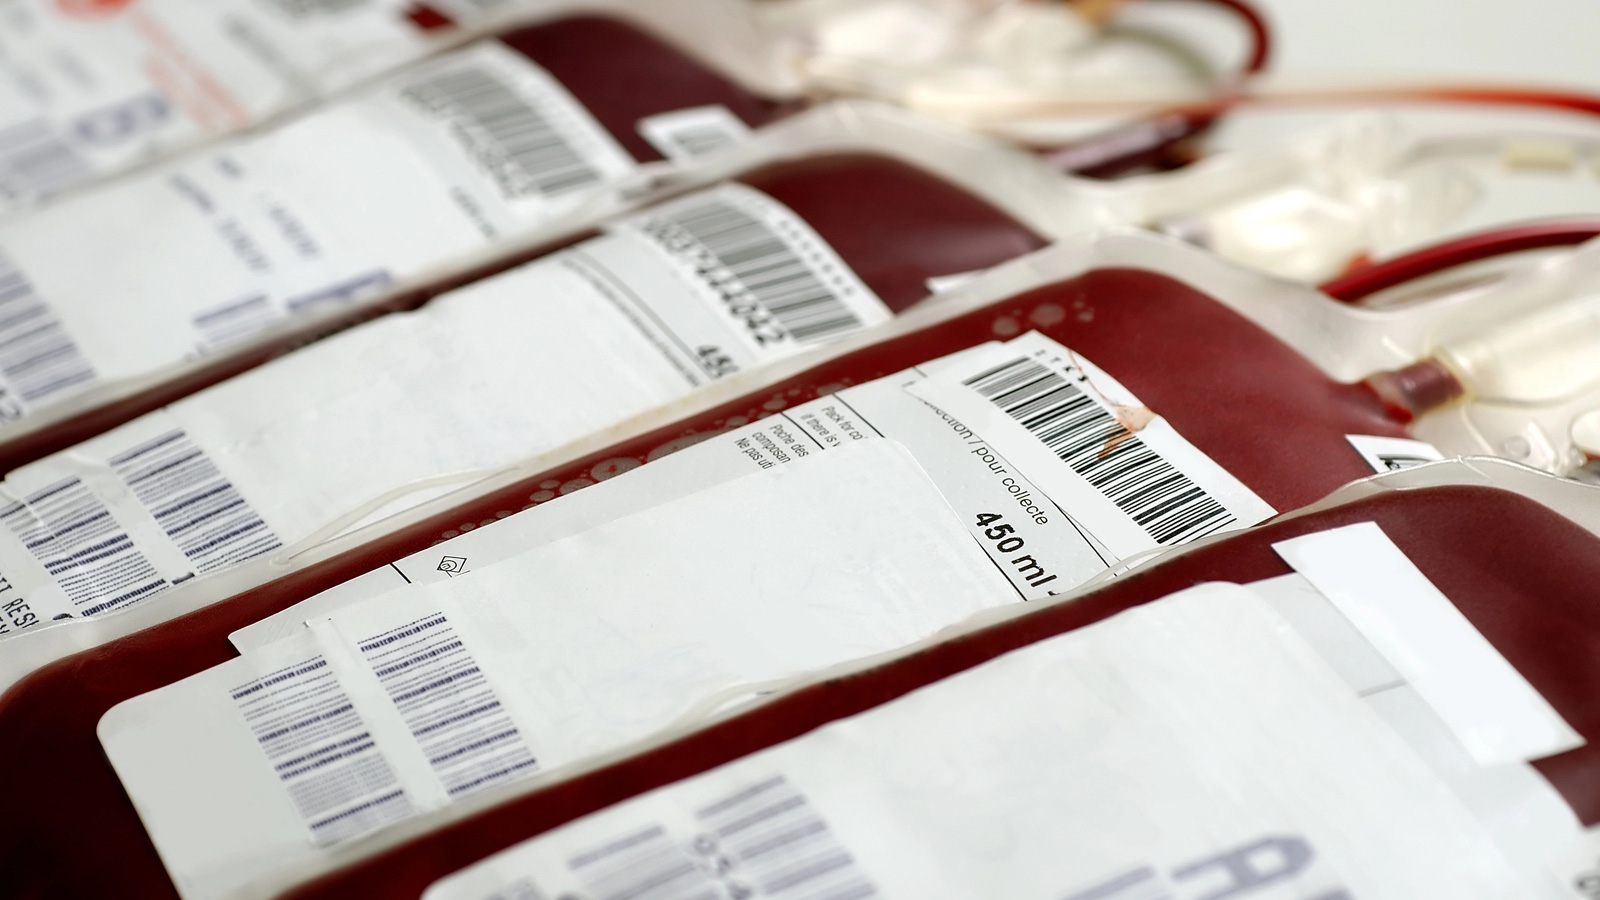
France's national blood service has confirmed that a cyberattack targeting a refrigeration equipment provider raised temperature and defrost settings at three of its facilities, threatening stored blood products.
The French Blood Establishment (Établissement français du sang or EFS), which manages blood collection, processing, and distribution across France, said the incident occurred on November 2 and affected systems used to monitor and control cold-storage chambers.
According to a statement published on November 3, EFS was not directly targeted in the cyberattack, but was instead its refrigeration supplier.

While EFS has not named the affected supplier, European refrigeration equipment provider Coolworld Rentals confirmed in a statement that a cybersecurity incident involving remote monitoring software had affected a limited number of its refrigeration units.
Coolworld says the attackers exploited a vulnerability in a third-party component, which was outside the company's direct control.
"The vulnerability currently being reported in the media relates to a component from a third-party supplier and was outside Coolworld's direct control," the company said.
"Only a limited number of Coolworld units were affected, and Coolworld responded promptly and took appropriate measures."
The company said it is working with affected customers but will not comment on individual cases.
At EFS, the incident raised temperature and defrost thresholds in affected cold-storage chambers to extremely high levels.
These facilities store blood products before they are distributed to hospitals, as well as biological samples maintained by the EFS.
EFS says its monitoring and alarm systems quickly detected the temperature change, allowing staff to fix impacted equipment or transfer products to other refrigeration facilities.
"No health impact has been identified, and no loss of blood products has been reported," EFS said in its statement [translated from French].
The organization confirmed that plasma bags intended for transfusions and plasma used to manufacture medicines were either transferred or secured, preventing damage to the products.
Blood collection and distribution operations have continued without interruption.
EFS says its technical teams are working with France's national cybersecurity agency (ANSSI) and the Ministry of Health, and it has strengthened monitoring of refrigeration equipment and temperatures.
The incident follows a wave of cyberattacks targeting refrigeration systems across Europe, where attackers remotely manipulate temperature settings or activate defrost functions that turn off cooling.
In October, cyberattacks disrupted refrigeration systems at an estimated 250 to 350 French supermarkets, including Intermarché, Carrefour Market, Monoprix, Leclerc, and Super U.
In those attacks, hackers reportedly compromised refrigeration controllers running older Danfoss software and remotely activated automatic defrosting functions, raising temperatures and forcing stores to discard fresh and frozen products.
These attacks targeted Danfoss AK-SM/AK-SC and Copeland/Dixell XWEB refrigeration controllers, which are used to monitor and manage cooling equipment remotely.
A second wave of attacks occurred this month, affecting more than 115 stores across Belgium, the Netherlands, Sweden, Luxembourg, Ireland, and Estonia.
Some refrigeration systems were shut down entirely, while others had their temperature settings changed remotely.
At one Swedish supermarket, the system reportedly began generating heat, while another store reported that temperatures were changed to 50°C (122°F).
Belgian refrigeration company Sabcobel previously said that attackers behind the November incidents exploited the same vulnerability used in October's attacks against French supermarkets.
In 2025, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) disclosed two vulnerabilities affecting Danfoss AK-SM 8xxA controllers, tracked as CVE-2025-41450 and CVE-2025-41451.
The flaws could allow attackers to bypass authentication and execute commands remotely on vulnerable systems, potentially giving them control over refrigeration equipment.
However, it has not been confirmed whether these vulnerabilities are being exploited in the attacks.

Uncover email threats your existing defenses may miss.
Adaptive Security's AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what's getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.
Start your free email security scan.Originally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.