WordPress backup plugin flaw exposes millions of sites to takeover attacks
An SQL injection vulnerability in the All-in-One WP Migration and Backup plugin for WordPress could allow unauthenticated attackers to execute remote code and take control of affected websites. [...]
WordPress backup plugin flaw exposes millions of sites to takeover attacks
Bill Toulas
- September 2, 2026
- 03:28 PM
An SQL injection vulnerability in the All-in-One WP Migration and Backup plugin for WordPress could allow unauthenticated attackers to execute remote code and take control of affected websites.
The plugin is used to back up, export, import, and move entire websites, including their databases, media, themes, and plugins, between servers or domains.
The security flaw is tracked as CVE-2026-19949 and received a high-severity score. It was discovered by security researcher Jack Taylor, who reported it in mid-August through Defiant's cybersecurity branch, Wordfence.
In a report yesterday, Wordfence researchers say that CVE-2026-19949 is a second-order SQL injection vulnerability that impacts All-in-One WP Migration and Backup versions throuhg 7.109.
The issue consists of incorrect parsing of escaped backslashes and quotation marks while the plugin rewrites database content during archive restoration.
An unauthenticated attacker could plant crafted data through WordPress trackbacks, which would execute when an administrator exports and imports the site, both common operations for the plugin.
The injected SQL can expose the plugin’s secret import key (ai1wm_secret_key) through a public comment, allowing the attacker to obtain it and import a malicious ‘.wpress’ archive containing executable code.
Wordfence mentions that code execution at this privilege level may lead to taking complete control of the target website.
According to statistics from WordPress.org, All-in-One WP Migration and Backup has more than five million active installations.
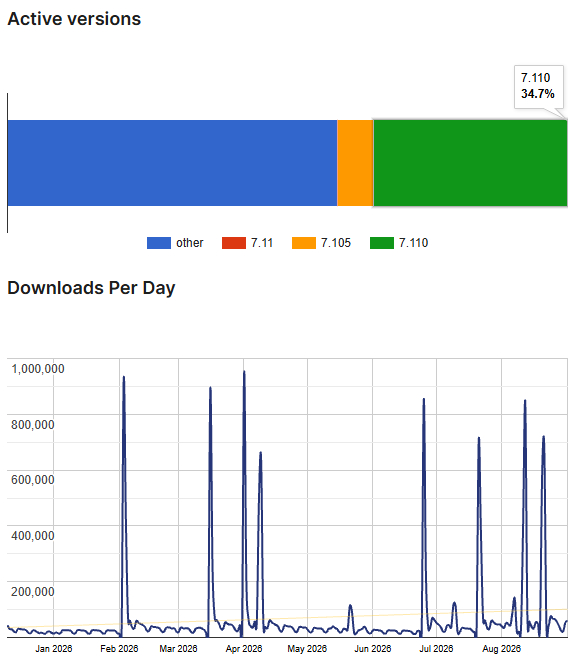
Since the vendor fixed the issue, only approximately 35% of the plugin’s user base has updated to the latest version, with the remaining 3.25 million sites running a vulnerable release of All-in-One WP Migration and Backup.
source: BleepingComputer
Exploit triggered by admin action
The payload that triggers the exploit remains dormant until the administrator restores a backup archive, an action that causes the processing of SQL string boundaries to execute the stored data as SQL.
While this prerequisite lessens the immediate risk of exploitation, Wordfence notes that, given the plugin’s role, it is to be expected that admins perform the action at some point.
“Since backup and restore is the core purpose of this plugin, this is a routine action, but the injected SQL will not execute until it takes place,” Wordfence notes.
The researchers explain that a deactivated vulnerable version of the plugin poses less risk, but it can still be exploited if temporarily activated.
Wordfence disclosed the issue to the developers of the All-in-One WP Migration and Backup plugin, ServMask, on August 15, after validating Taylor’s finding.
On August 20, ServMask addressed the CVE-2026-19949 vulnerability in version 7.110 of the plugin.

Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
Get the reportOriginally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.