Vercel rolls out new protection against stolen session cookie attacks
Vercel is gradually rolling out Device Bound Session Credentials (DBSC) on its platform as a key defense against information stealer malware. [...]
Vercel rolls out new protection against stolen session cookie attacks
Bill Toulas
- November 4, 2026
- 04:31 PM

Vercel is gradually rolling out Device Bound Session Credentials (DBSC) on its platform as a key defense against information stealer malware.
The new feature, announced by Vercel's CTO Malte Ubl on X, binds a login session to the user's device with a private key stored in a TPM, so even if the session cookie is stolen, it can't be reused on another device.
Vercel is a cloud platform developers use to deploy and host websites, web applications, and AI agents. The company also develops the popular Next.js web framework.

Its latest announcement concerns logins to Vercel's platform at vercel.com, where developers manage their projects and deployments.
"DBSC works by storing a private key in your device's TPM (the same device that the fingerprint sensor or similar biometric devices on your laptop or phone uses) and using that key to sign your cookie," explained Ubl.
"The private key can never be retrieved ever again. Not by us, not by you, not by the malware."
Vercel's DBSC rollout also complements Chrome's App-Bound Encryption, which makes it harder for infostealer malware to extract browser cookies. DBSC adds another layer of protection by preventing stolen session cookies from being reused on other devices.
DBSC currently works in Chrome on macOS and Windows, but the rollout is gradual to ensure edge cases involving OAuth apps are handled appropriately.
Separately, Vercel is rolling out a similar protective technology called DPoP for the Vercel CLI.
Security Review also lands
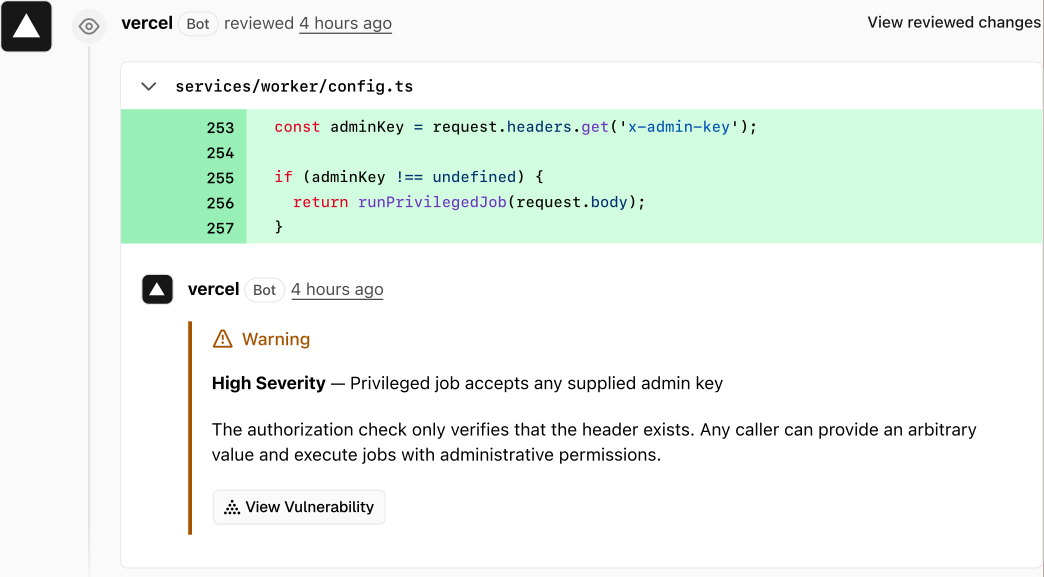
Earlier this week, Vercel launched Security Review in public beta for Pro and Enterprise teams, adding a feature to Vercel Agent that scans code changes on every push to connected GitHub repositories once enabled.
The new system uses code and team-defined policies to flag issues such as missing authorization checks and exposed secrets.
If permissions allow, the Vercel Agent can validate and commit fixes.
Source: Vercel
Vercel says Security Review scans will be free until November 10, 2026, while agent-generated fixes will be billed separately.
Ubl said that Vercel's security team shipped this new feature internally a couple of months back, and it has already proven its worth, so the platform decided to make it broadly available.
In April, Vercel suffered a security breach impacting a subset of customers, in which attackers gained access to its systems by compromising an employee's Google Workspace account at Context.ai.
Vercel said the attacker used that access to reach internal systems and view environment variables that hadn't been marked as sensitive.
A threat actor impersonating ShinyHunters attempted to sell the allegedly stolen source code, access keys, and database data.
Uncover email threats your existing defenses may miss.
Adaptive Security's AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what's getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.
Start your free email security scan.Originally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.