Targeted ads installed Candiru spyware in zero-click attacks
Candiru spyware was delivered to devices at Al Jazeera Media Network via targeted online advertisements in a zero-click attack that required only rendering the malicious ads on the victim's device. [...]
Targeted ads installed Candiru spyware in zero-click attacks
Bill Toulas
- October 16, 2026
- 01:20 PM
Candiru spyware was delivered to devices at Al Jazeera Media Network via targeted online advertisements in a zero-click attack that required only rendering the malicious ads on the victim's device.
Researchers at Citizen Labs investigating the attacks referred to this technique as AdFection, noting that their report is the first public technical confirmation of mercenary spyware delivered through targeted ads.
A similar method was documented in late 2025 by Amnesty International, involving ads that infected targets with Predator spyware without them clicking anything.
That infection mechanism was called Aladdin and surfaced due to a collection of marketing files and documents leaked from the Intellexa surveillance company that researchers studied and corroborated with technical details from forensic investigations.
Unlike Alladin, AdFection was caught in real attacks and linked to Israeli firm Discovere-Tech, described by Citizen Lab as " a bridge between mercenary spyware companies and the advertising ecosystem."
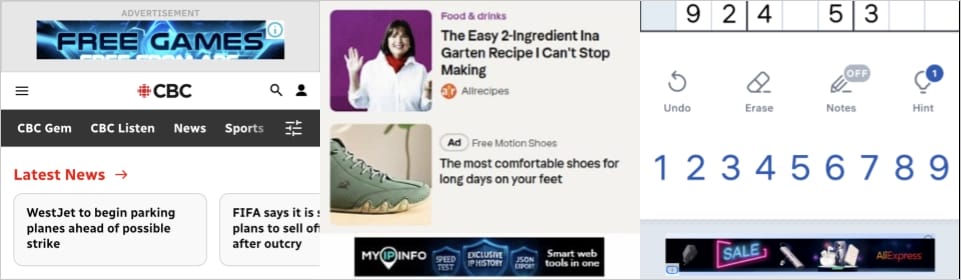
Source: Citizen Lab
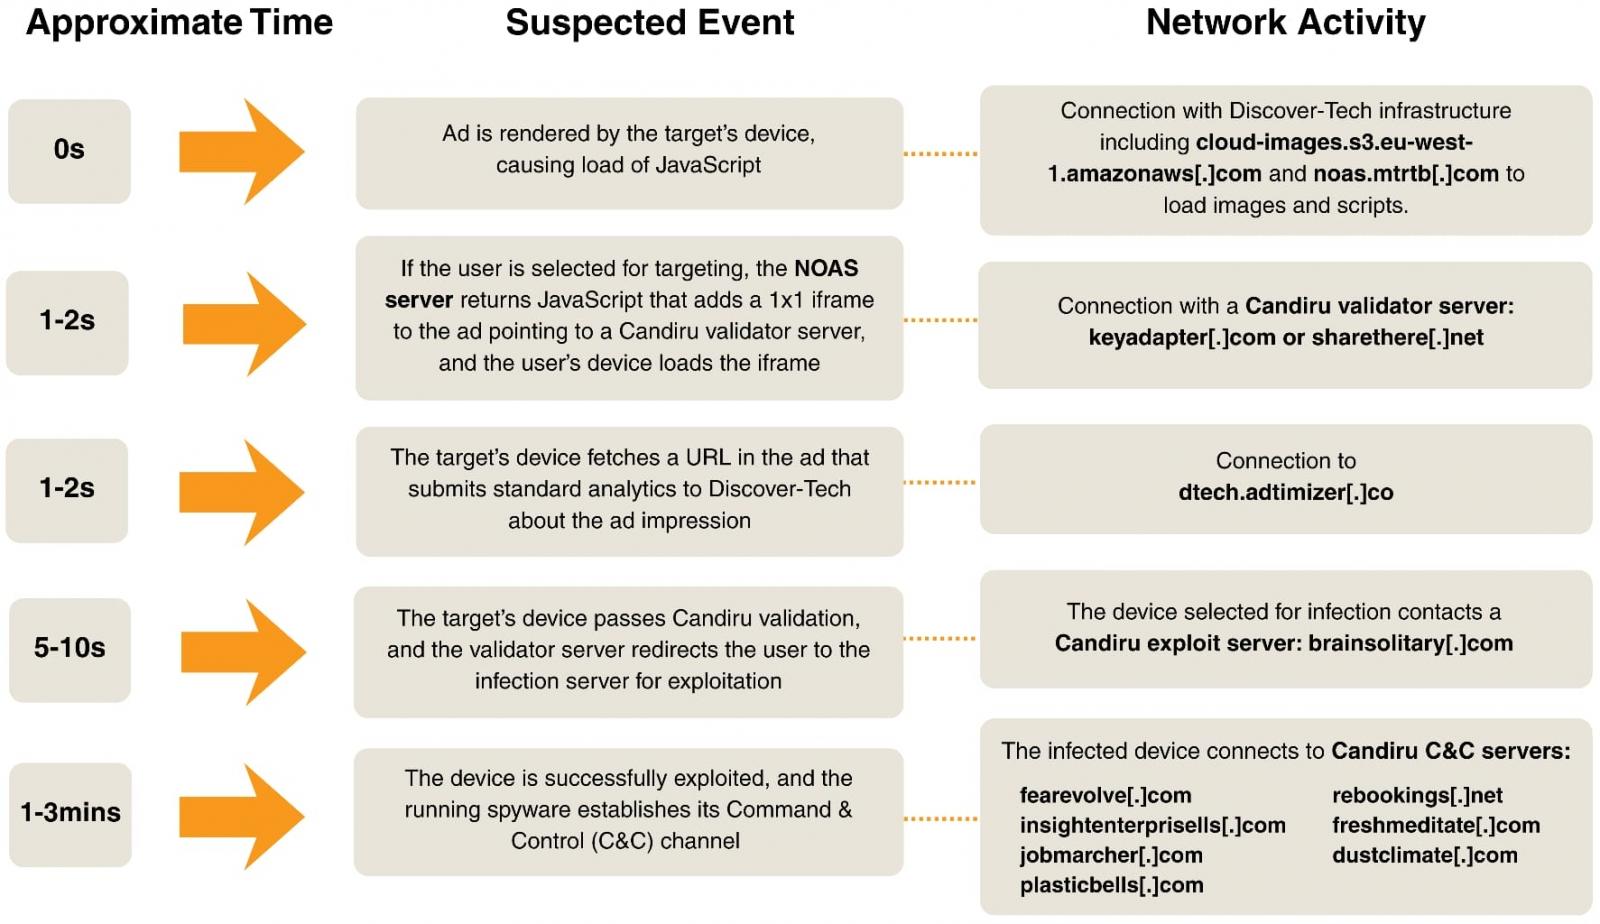
Zero-click Candiru spyware infection
According to Citizen Lab, Discover-Tech allowed its customers to use its Controlium platform to target specific devices with malicious code, or profile, deanonimize, and fingerprint user devices.
"Discover-Tech appears to work with multiple mercenary spyware, hacking, and advertising vendors, connecting the spyware industry to the online advertising ecosystem," Citizen Lab says.
The company purchased ad placements through mainstream ad networks and exchanges, embedding JavaScript in ads that contacted its "NOAS server" when rendered.
Using multiple parameters (e.g., IP address, ad identifiers), the NOAS server, "or getAd server," determined if a target was eligible to receive JavaScript code.
Selected targets received additional code, while other devices the ad rendered on received nothing, helping keep the attacks stealthy.
Source: Citizen Lab
Al Jazeera provided Citizen Lab with evidence of attacks that targeted at least 45 devices between 2024 and 2025. The network logs examined by the researchers showed a sequence from Discover-Tech infrastructure to Candiru validation servers and then to spyware command-and-control servers.
The researchers also recovered a DLL file from a compromised Windows system and attributed it with high confidence to Candiru, based on infrastructure and code overlaps with previously captured samples.
Candiru is an Israeli spyware vendor that sells surveillance tools, officially only to governments. The company also developed malware for Windows called DevilsTongue, which can steal files, credentials, and messages.
According to past reports, its tools have been deployed through Windows and Chrome zero-day exploits against journalists, activists, politicians, and other targets.
Source: Citizen Lab
While Al Jazeera is one confirmed target of these attacks, Citizen Lab reports that the advertising operation placed 3.77 billion bids and won 442 million auctions between March and June 2026.
Ads assessed to carry attacker script tags appeared across 75,373 Android/iOS apps and 120,768 websites, although these figures do not represent infection counts.
“We estimate that between hundreds of thousands and millions of users were directed to these domains via Discover-Tech ads,” explains Citizen Lab.
After receiving Citizen Lab's reports, major advertising companies like Google, IAB Europe, Beeswax, Eskimi, and Vungle took action to remove offending accounts and block access to domains.
Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
Get the reportOriginally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.