NVIDIA confirms GeForce NOW data breach affecting Armenian users
NVIDIA has confirmed in a statement for BleepingComputer that GeForce NOW user information has been exposed in a data breach. [...]
NVIDIA confirms GeForce NOW data breach affecting Armenian users
Bill Toulas
- May 8, 2026
- 12:18 PM
NVIDIA has confirmed in a statement for BleepingComputer that GeForce NOW user information has been exposed in a data breach.
The gaming and hardware giant has clarified that the impact is limited to Armenia, and was caused by a compromise of the infrastructure operated by a regional partner.
The company added that its own network was not impacted by the incident.
“Our investigation found no impact on NVIDIA-operated services. The issue is limited to systems run by a third-party GeForce NOW Alliance partner based in Armenia. We are working closely with the partner to support their investigation and resolution. Impacted users will be notified by GFN.am,” the company said.
The statement comes in response to a post last week on a hacker forum from a threat actor using the ShinyHunters nickname, claiming to have breached the GeForce NOW service and stolen millions of user records.
However, the ShinyHunters actor who published the breach on the hacker forum is believed to be an imposter.
According to the threat actor, the stolen information includes full names, email addresses, usernames, dates of birth, membership status, and 2FA/TOTP status.
The threat actor also posted samples of the stolen data and offered the full database for $100,000 paid in Bitcoin or Monero.
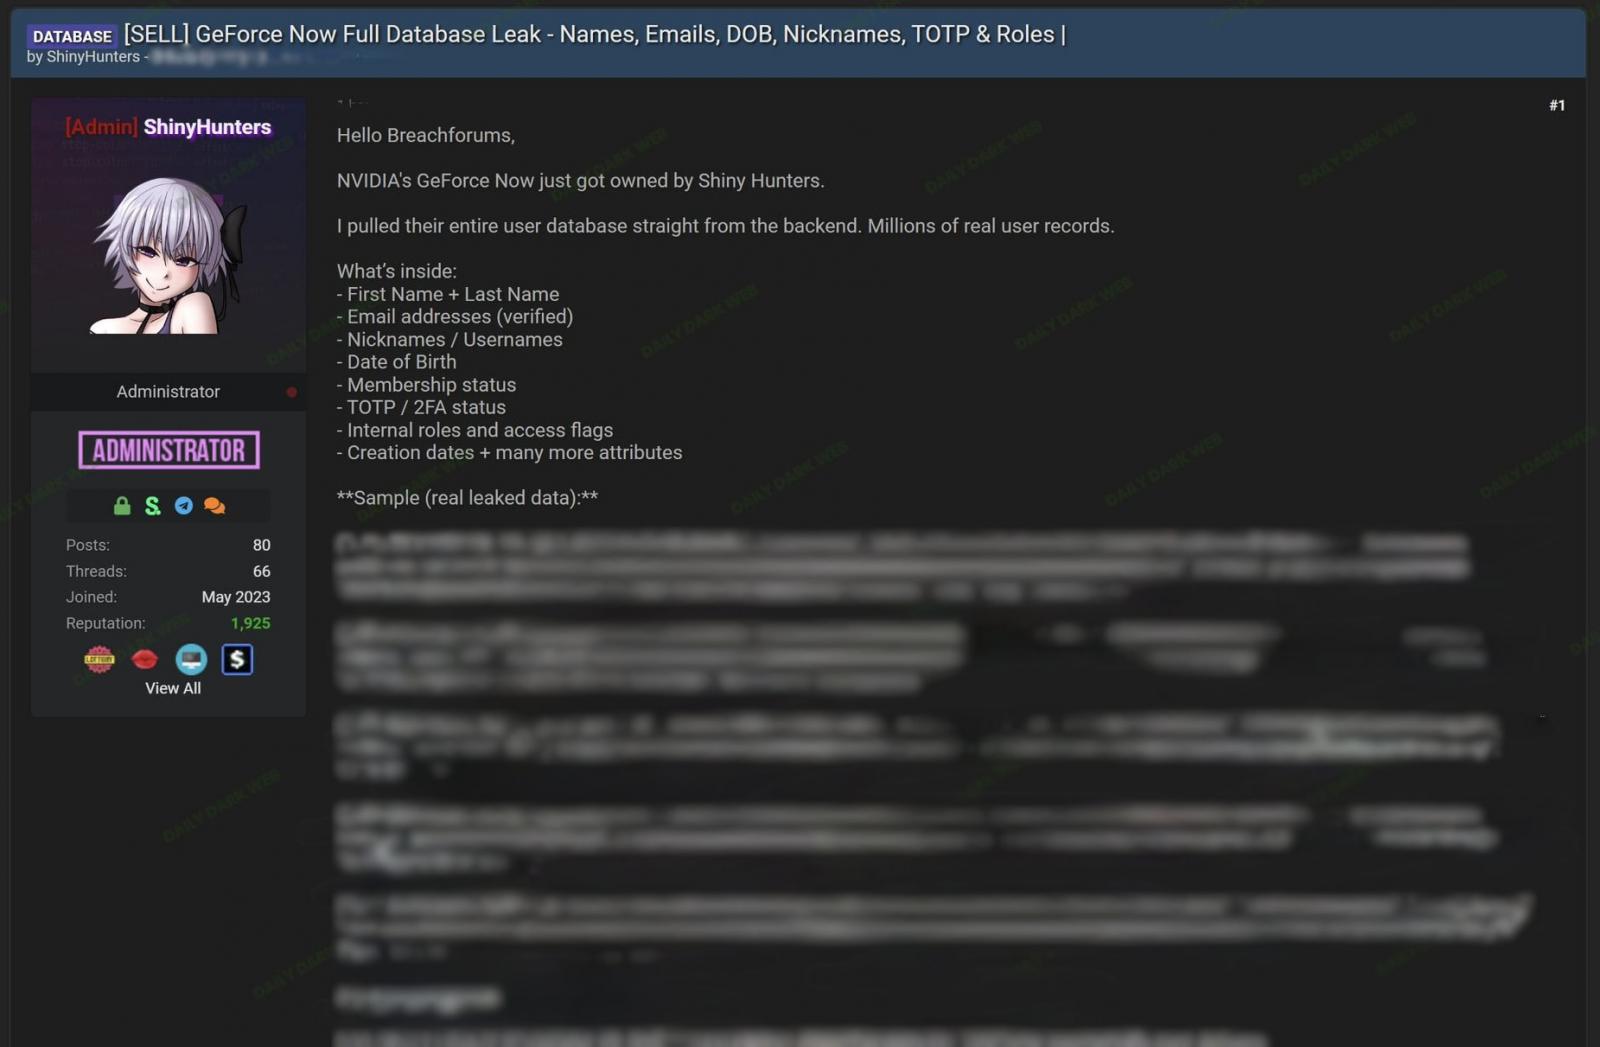
Source: DailyDarkWeb
The NVIDIA GeForce NOW cloud gaming service lets users stream to their systems games running on more powerful hardware using NVIDIA GPUs in a datacenter.
GFN.am is the Armenian regional operator for GeForce NOW, responsible for operating NVIDIA’s service in the country.
Alliance partner environments can operate independent authentication systems, local customer databases, regional billing platforms, and locally managed infrastructure.
A statement posted by GFN.am confirms a cybersecurity incident that took place between March 20 and 26 and exposed the following information:
- Full name (if using a Google account)
- Email address
- Phone number (if registered through a mobile operator)
- Date of birth
- Username
GFN.am has clarified that no account passwords were exposed in the incident, and any users who registered to the service after March 9 are not impacted.
According to NVIDIA’s help page, GFN.am is also responsible for managing GeForce NOW operations in Azerbaijan, Georgia, Kazakhstan, Moldova, Ukraine, and Uzbekistan, but no impact on those countries has been confirmed.
BleepingComputer found that the threat actor’s post has now been removed from the hacker forum.
It is unclear if the database has been sold to a buyer or if the seller or forum administrators deleted it.
Update [14:14]: Added information that the threat actor may be a ShinyHunters impersonator.
99% of What Mythos Found Is Still Unpatched.
AI chained four zero-days into one exploit that bypassed both renderer and OS sandboxes. A wave of new exploits is coming.
At the Autonomous Validation Summit (May 12 & 14), see how autonomous, context-rich validation finds what's exploitable, proves controls hold, and closes the remediation loop.
Claim Your SpotOriginally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.