Microsoft’s X account hacked in crypto pump-and-dump scheme
On Thursday, unknown attackers hijacked the official Microsoft account on X, which has over 13 million followers, in what appeared to be a pump-and-dump scheme promoting a crypto token. [...]
Microsoft’s X account hacked in crypto pump-and-dump scheme
- October 2, 2026
- 05:29 AM
On Thursday, unknown attackers hijacked the official Microsoft account on X, which has over 13 million followers, in what appeared to be a pump-and-dump scheme promoting a crypto token.
The attack began when the Microsoft account (@Microsoft) followed and reposted a tweet from another now-suspended X account (@clippymsftcto) impersonating Microsoft's Clippy virtual assistant, The Verge first reported.
While @clippymsftcto has been suspended, another X account (@ClippyMSFT) that reposted Microsoft's tweet is still promoting a $Clippy crypto token, claiming that it has "has a liquidity pool paired directly with $MSFT."
Microsoft has since removed the attackers' posts and confirmed the incident, saying it's investigating the circumstances.
"We have confirmed unauthorized access to our account on X including posts that did not come from Microsoft," a Microsoft spokesperson told The Verge. "The account has been secured and the unauthorized posts have been removed, and we are continuing to investigate the circumstances."
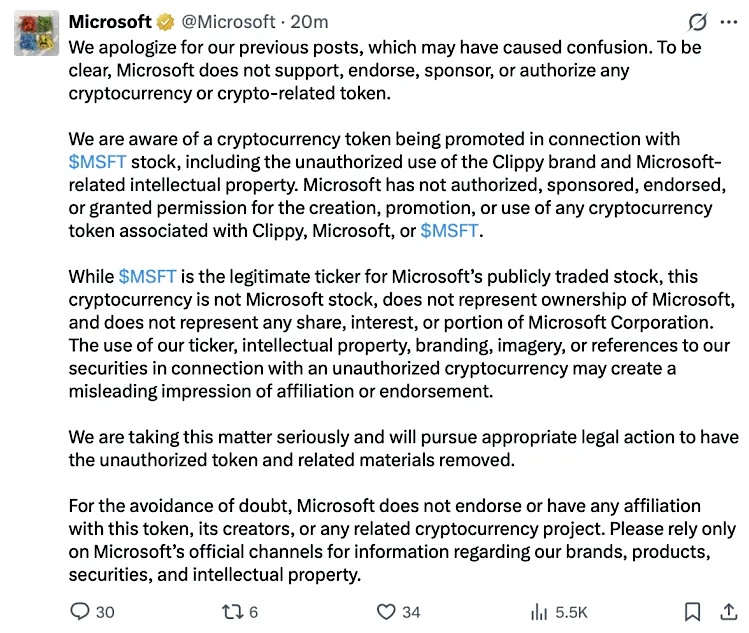
In a now-deleted tweet, the company also apologized for the posts and said that it doesn't support any cryptocurrency or crypto-related token and will take legal action.
"We are aware of a cryptocurrency token being promoted in connection with $MSFT stock, including the unauthorized use of the Clippy brand and Microsoft-related intellectual property. Microsoft has not authorized, sponsored, endorsed, or granted permission for the creation, promotion, or use of any cryptocurrency token associated with Clippy, Microsoft, or $MSFT," Microsoft said.
"We are taking this matter seriously and will pursue appropriate legal action to have the unauthorized token and related materials removed. For the avoidance of doubt, Microsoft does not endorse or have any affiliation with this token, its creators, or any related cryptocurrency project."
A Microsoft spokesperson was not immediately available to comment when BleepingComputer reached out earlier today for more details on the incident.
This isn't the first time an official Microsoft X account has been hacked. In June 2024, crypto scammers also hijacked the Microsoft India account on X (@MicrosoftIndia), with over 211,000 followers, to impersonate Roaring Kitty, the handle of notorious meme stock trader Keith Gill.
The attackers used the compromised account to lure potential victims and infect them with cryptocurrency wallet drainer malware.
They also used the hijacked account to reply to tweets, luring Microsoft India's followers and others on X to a malicious website (presaIe-roaringkitty[.]com) that allegedly allowed them to buy GameStop (GME) crypto as part of a so-called presale.
However, the attackers stole the crypto assets of anyone who connected their cryptocurrency wallets to the site and authorized transactions to the drainer service.
In recent years, X users have been targeted by a massive wave of account hijacks and malicious ads, with verified organizations falling victim to hacks promoting cryptocurrency scams and wallet drainers.
To put things into perspective, blockchain threat analysts at ScamSniffer revealed in December 2023 that cybercriminals stole roughly $59 million worth of cryptocurrency from 63,000 people in a single Twitter ad push between March and November using the "MS Drainer" wallet drainer.
Last year, the U.S. Securities and Exchange Commission's @SECGov account was also compromised in a SIM-swapping attack. The compromised account posted a fake announcement about the long-awaited approval of Bitcoin exchange-traded funds (ETFs) on security exchanges, which caused a temporary but significant spike in Bitcoin prices.
Eric Council Jr., the hacker behind the @SECGov hijack, pleaded guilty in February 2025 and was sentenced to 14 months in prison for his role in a conspiracy that used the compromised account to manipulate Bitcoin's value.

Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Save your seatOriginally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.