Medtronic confirms breach after hackers claim 9 million records theft
Medical device giant Medtronic disclosed last week that hackers breached its network and accessed data in "certain corporate IT systems." [...]
Medtronic confirms breach after hackers claim 9 million records theft
Bill Toulas
- April 27, 2026
- 09:50 AM
Medical device giant Medtronic disclosed last week that hackers breached its network and accessed data in “certain corporate IT systems.”
The confirmation comes after the infamous data extortion group ‘ShinyHunters’ claimed the intrusion and the theft of more than 9 million records from the company.
Medtronic is an international medical equipment giant with 90,000 employees and operations in 150 countries. It is the largest medical device maker in the world by revenue ($33.5 billion) and also develops healthcare technologies and therapies.
Medtronic disclosed the incident on its website, saying that the breach did not impact customers or products and that business operations remained unaffected.
“We have not identified any impact to our products, patient safety, connections to our customers, our manufacturing and distribution operations, our financial reporting systems, or our ability to meet patient needs,” reads Medtronic's announcement.
“The networks that support our corporate IT systems, our products and our manufacturing and distribution operations are separate.”
“Hospital customer networks remain separate from Medtronic IT networks and are secured and managed by customers’ IT teams.”
Although Medtronic did not provide additional information about the attack or its perpetrators, threat actor ShinyHunters listed the company among its victims, stating that their breach resulted in the theft "over 9 million records containing PII [personally identifiable information]."
The threat actor also claims to have compromised "terabytes of internal corporate data" and pressured the company to pay under the threat of a leak.
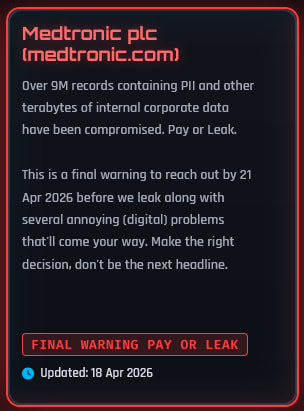
The hackers listed Medtronic on April 18 and threatened to release the stolen data unless the company engaged in negotiations for a ransom payment by April 21.
Currently, Medtronic is no longer visible on ShinyHunters' data leak site.
BleepingComputer has contacted Medtronic with questions, and we will add an update to this post when we receive a response.
Meanwhile, the company stated that an investigation is underway to determine whether any personal data has been accessed by the hackers.
If customer data exposure is confirmed, Medtronic will send notifications and provide support services to those who need them, the company promised.
99% of What Mythos Found Is Still Unpatched.
AI chained four zero-days into one exploit that bypassed both renderer and OS sandboxes. A wave of new exploits is coming.
At the Autonomous Validation Summit (May 12 & 14), see how autonomous, context-rich validation finds what's exploitable, proves controls hold, and closes the remediation loop.
Claim Your SpotOriginally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.