JWK and X.509 answer different questions about a public key
A JSON Web Key and an X.509 certificate can both expose public key information. That does not make them interchangeable trust objects. If you are integrating an API, first separate the key representation from the reason

A JSON Web Key and an X.509 certificate can both expose public key information. That does not make them interchangeable trust objects. If you are integrating an API, first separate the key representation from the reason your application accepts that key.
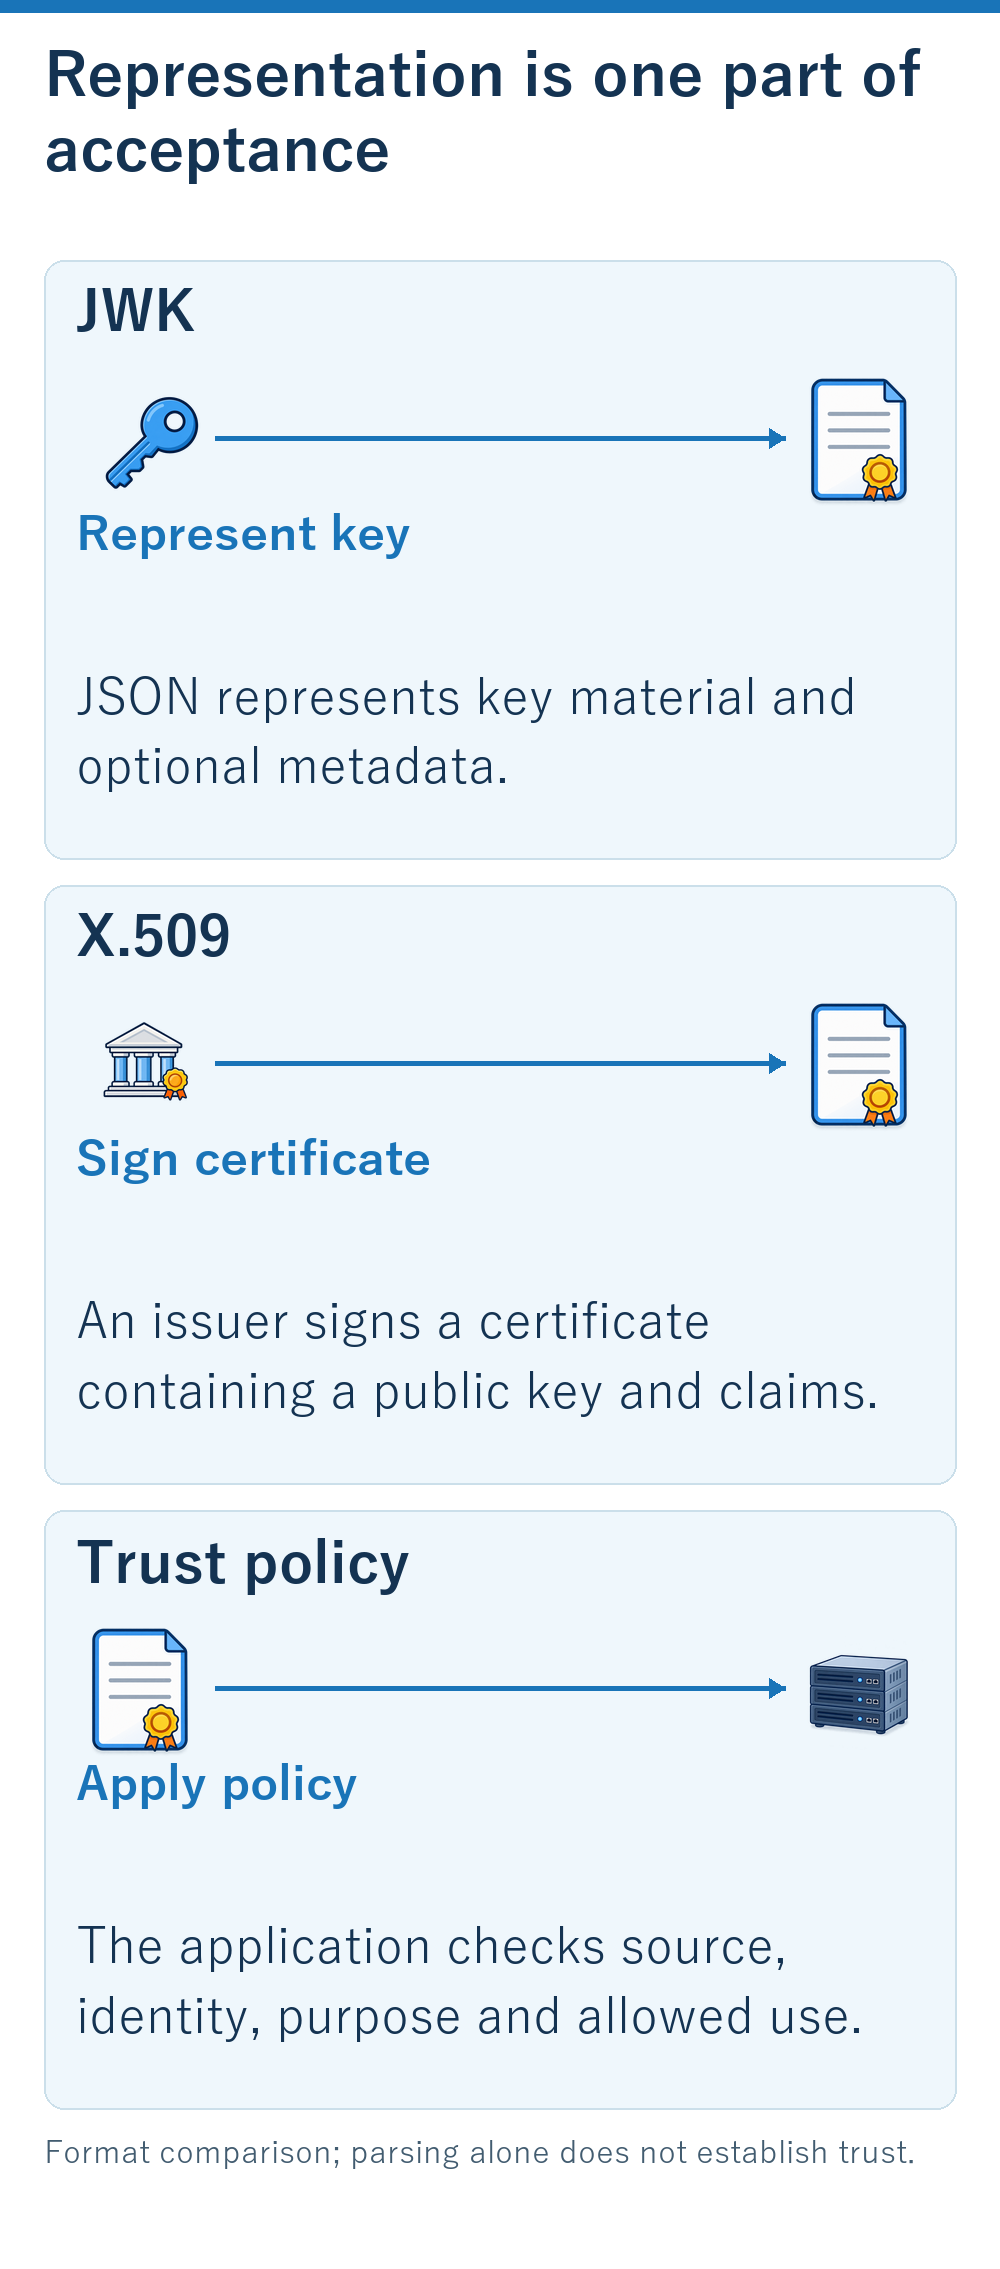
Format comparison; parsing alone does not establish trust.
Start with the representation
JWK is a JSON representation of a cryptographic key. Its members describe the key type and key material, with optional metadata. Some JWKs contain private parameters, so a file being JSON does not make it safe to publish.
X.509 certificates package a public key with other information and an issuer signature. Their acceptance depends on certificate path validation and application-specific checks.
Ask where trust enters
If an application downloads a JWK Set from a trusted configuration endpoint, the trust relationship includes how that endpoint was selected and protected. A key identifier such as kid helps select a key; it does not independently prove that the key is authorized.
A certificate also needs an accepted trust path and appropriate identity and purpose checks. Merely parsing either format is not a trust decision.
Understand the optional bridge
JWK can include an x5c member containing a certificate chain. That creates a relationship between formats, but it does not remove the need to check consistency or validate the chain according to the application’s rules.
Avoid treating a supplied chain as a new trust anchor just because it arrived alongside the key. The sender should not get to choose the verifier’s trust policy implicitly.
Write a key intake note
For an API integration, document format, source URL or configuration source, permitted algorithms, expected issuer or identity, rotation method and failure behavior. Include whether private material is allowed in that location.
The result should explain both how to read the key and why to accept it. That is a more useful beginner deliverable than memorizing which file extension belongs to which format.
Primary sources
Further reading on PKI Channel
The following Japanese-language guides add diagrams and operational detail to the questions discussed above.
AI was used for research assistance, writing and illustration. Examples and checklists are explanatory, not reported lab results.
Originally published by Dev.to Security. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.