Hirudo Android malware replaces banking apps to evade security checks
A new Android malware called Hirudo steals bank account credentials by replacing legitimate banking apps with modified versions that disable security checks. [...]
Hirudo Android malware replaces banking apps to evade security checks
Bill Toulas
- October 14, 2026
- 07:41 AM
A new Android malware called Hirudo steals bank account credentials by replacing legitimate banking apps with modified versions that disable security checks.
Researchers identified malicious copies of eight banking apps that use a hooking engine to bypass app-signature, Accessibility, and Play Integrity checks by substituting certificate information or returning empty lists.
Threat actors can use Hirudo to steal credentials, remotely control infected phones in real time, collect messages, capture screenshots, and record audio.
A report today from mobile security company ThreatFabric notes that Hirudo has been observed impersonating at least seven Indonesian banks, but the malware also targets financial organizations in China, India, Mexico, Morocco, and Thailand.
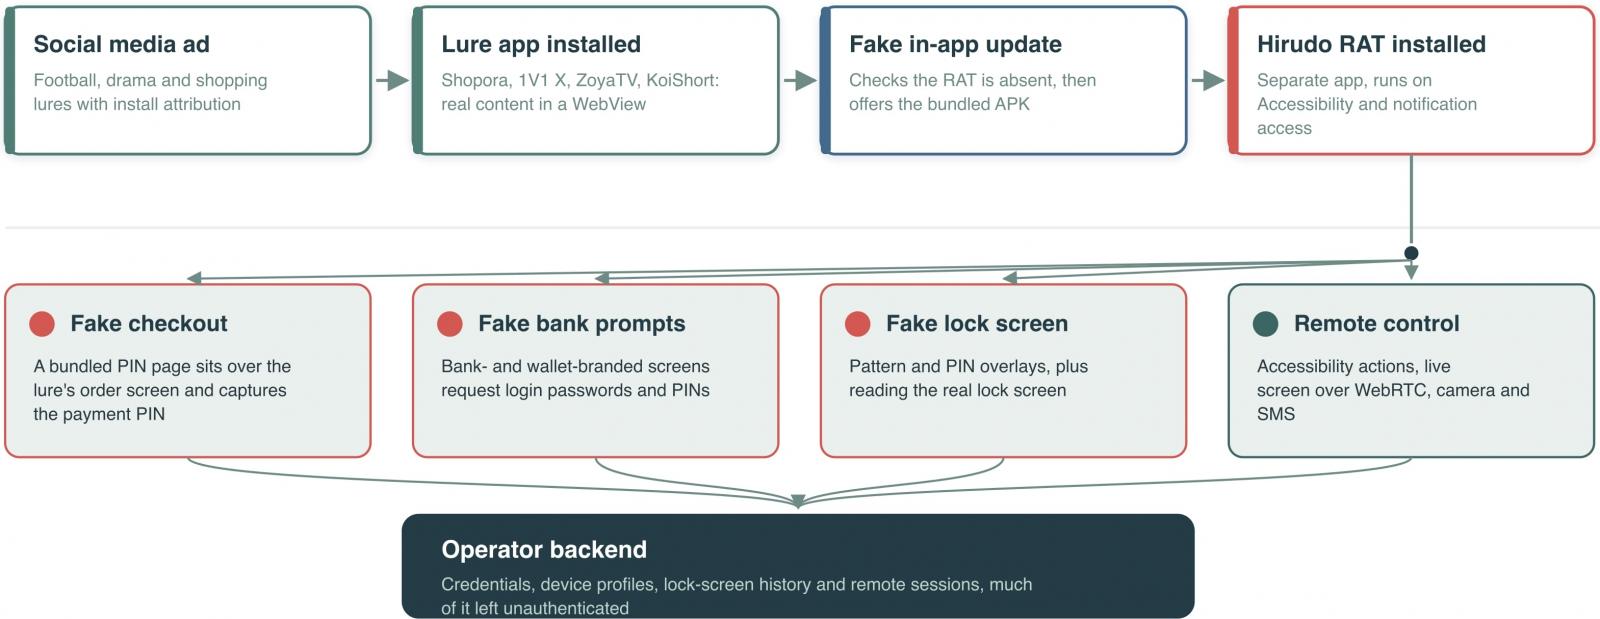
The malware is typically delivered via apps for shopping (Shopora), adult content (1V1 X), or short drama (ZoyaTV, KoiShort) that appear legitimate and provide the promised functionality.
The researchers say that these apps act as malware loaders for Hirudo, showing a fake “update” notification that leads to permission-granting prompts, including for Accessibility services
Source: ThreatFabric
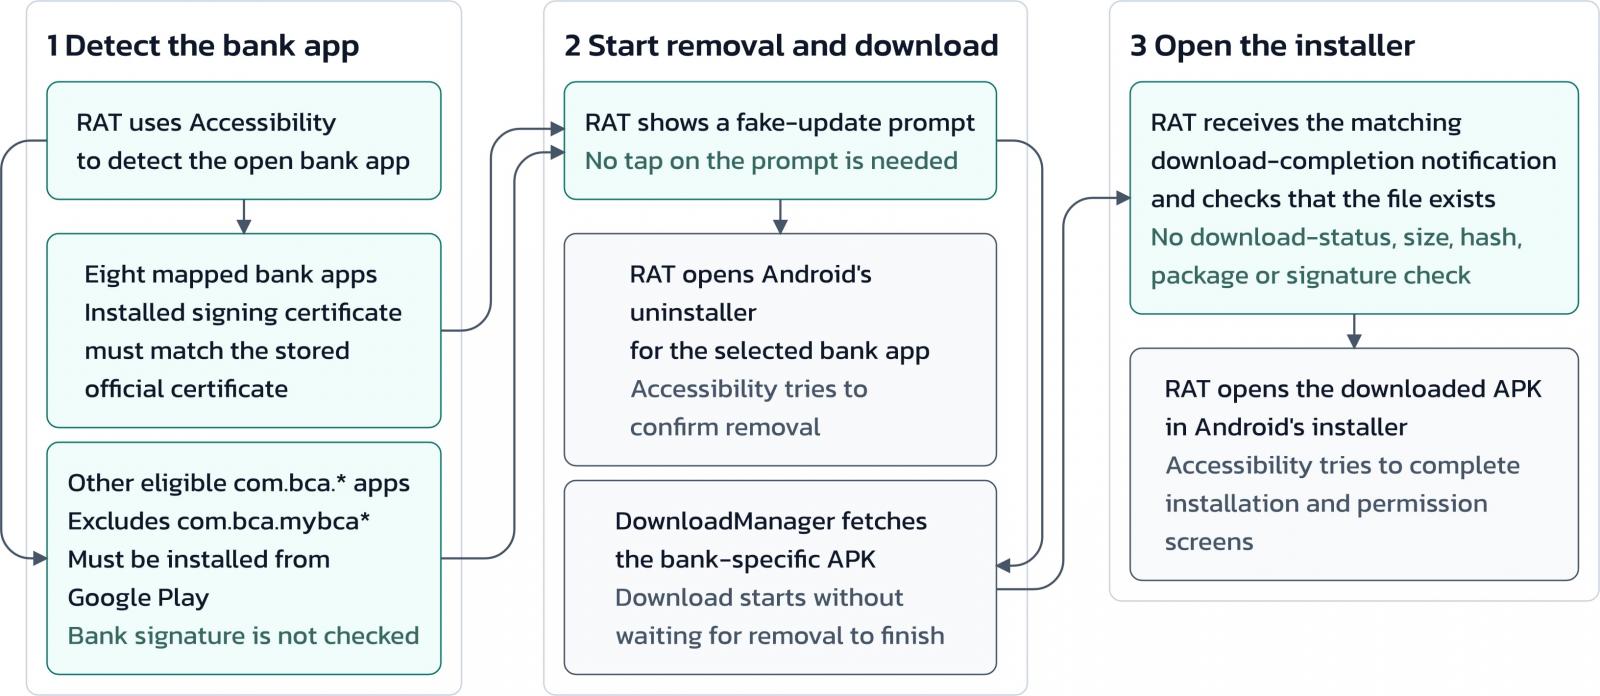
Once installed, Hirudo launches the real banking app’s uninstaller, downloads a patched copy, and abuses its Accessibility permission to install it.
ThreatFabric explains that this is a delicate, risky process for the malware, since the victim can interrupt it at two points.
Source: ThreatFabric
ThreatFabric found that the malicious copy of a banking app retains almost all of the original app’s code, but loads a hooking engine built on the open-source frameworks YAHFA and Dobby.
When launched, the patched app performs the following evasion actions:
- Substitute the genuine signing certificate when queried.
- Hide enabled Accessibility services.
- Remove screenshot protection, allowing remote viewing and recording.
- Modify key-attestation certificates and relay Play Integrity requests through an operator-controlled server.
“With the engine running inside the banking app's own process, the app's defenses are turned against it,” the researchers say.
Source: ThreatFabric
However, ThreatFabric explains there are certain limitations to these evasion methods.
The bundled attestation keybox has been publicly leaked, and Google lists two of its certificates as compromised, so server-side revocation checks can detect those forgeries.
Once active on the device, Hirudo can steal banking passwords, payment PINs, device-unlock secrets, and SMS messages, stream the screen to operators, and provide access to both cameras.
The malware’s fake checkout pages collect payment PINs, then display a fabricated payment-success result to deceive victims while it steals data.
Source: ThreatFabric
ThreatFabric found that Hirudo currently targets Indonesian banking apps and found thousands of application-credential entries in an unsecured backend panel, along with device, lock-screen, and financial-profile data. However, the victim count remains unknown.
According to the researchers, “Hirudo marks a deliberate escalation in how Android bankers approach hardened applications,” shifting the focus from device-level integrity checks to the security mechanisms built into banking apps.
The researchers suggest that banks should validate integrity and attestation server-side, bind checks to sessions and protected actions, and retain behavioral and transaction-risk controls.
Android users are strongly recommended to keep their devices up-to-date, avoid installing APK files sourced from unofficial Android stores, and periodically run Play Protect scans.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Save your seatOriginally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.