ASOS links data breach to social engineering attack, credential theft
ASOS is sending updates to affected customers about the cybersecurity incident it suffered earlier this week, confirming that hackers accessed some personal data. [...]
ASOS links data breach to social engineering attack, credential theft
Bill Toulas
- October 8, 2026
- 07:42 AM
UK fashion retailer ASOS confirmed that a recent data breach was caused by a social engineering attack in which hackers stole an employee’s login credentials and used them to access information on third-party platforms used by the company.
"We discovered that an unauthorised party gained access to an ASOS employee account by impersonating a trusted contact to obtain log in credentials," reads an ASOS security notification shared with BleepingComputer.
"Those credentials were then used to access information on certain third-party platforms used by ASOS."
The company locked down the affected platforms and launched an investigation with support from external experts, law enforcement, and regulatory authorities.
ASOS is a large UK-based online fashion retailer that sells clothing, footwear, accessories, and beauty products to customers worldwide.
On October 6, 2026, ASOS customers received a push notification through the ASOS app on their mobile devices, alleging customer data theft and urging the company’s staff to engage with them on Telegram.
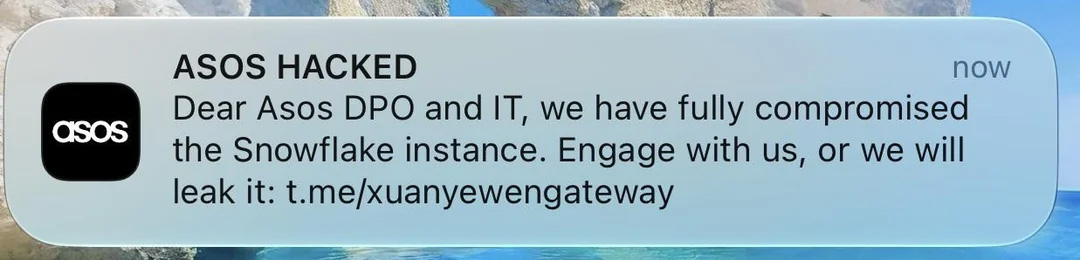
The threat actor, calling themselves “Xuanye Group,” claimed that they had stolen customer data, but not payment information.
ASOS eventually confirmed via a statement published on its website that it had suffered a data breach that may have exposed some “basic” personal information and contact details.
The latest update sent to customers confirms that the following details were exposed:
- Full names
- Contact details
- Certain non-personal account-related information
ASOS says hackers did not access payment card information or account passwords.
The retail giant also says its website and app were at all times, and continue to be, completely safe to use.
“There is no action you need to take on your account,” ASOS says in its message to customers.
“However, please remain cautious of unexpected messages or calls claiming to be from ASOS.”
“We will never ask you to share passwords, security codes or payment details through an unsolicited message or call.”
ASOS says its investigation is still underway, and it will share more updates if important findings emerge.
The company also assured that it has already taken steps to implement additional security measures to prevent similar incidents in the future.
BleepingComputer has asked ASOS about the number of customers impacted by this incident, but we have not received a figure yet.

Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Save your seatOriginally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.