Active ScreenConnect attacks breach MSPs, impact dozens of organizations
ConnectWise is investigating an active malware campaign targeting managed service providers (MSPs) that uses compromised ScreenConnect environments to deploy rogue remote-access clients to customer devices. [...]
Active ScreenConnect attacks breach MSPs, impact dozens of organizations
- November 11, 2026
- 05:56 PM
ConnectWise is investigating an active malware campaign targeting managed service providers (MSPs) that uses compromised ScreenConnect environments to deploy rogue remote-access clients to customer devices.
The campaign was first discovered Wednesday by cybersecurity firm Huntress, which says it has identified six compromised MSPs and 286 affected endpoints across 47 organizations, and that the number of victims continues to rise.
"Our SOC is working an active campaign that started around 17:47 UTC today targeting cloud-hosted ScreenConnect instances," Huntress posted to Reddit.
"We are currently tracking 6 compromised MSPs and 286+ endpoints, and those numbers are climbing. ConnectWise is engaged and working this with us."
ScreenConnect is a remote access and support platform used by MSPs and IT teams to remotely manage and troubleshoot customer devices.
According to Huntress, attackers are using ScreenConnect's Run Command functionality to deploy ScreenConnect clients on managed endpoints, providing remote access outside of the legitimate MSP's ScreenConnect environment.
The researchers also warned of a potentially more dangerous technique in which attackers can compromise an MSP technician's workstation when they initiate a ScreenConnect session with an infected customer device.
It is unclear how this reported reverse-pivot technique works, including whether it exploits a software vulnerability or abuses legitimate ScreenConnect functionality.
In a statement to BleepingComputer, ConnectWise confirmed it is investigating the attacks and urged partners to avoid interactive remote sessions with potentially compromised devices.
"We are aware of reports of malicious activity affecting a limited number of ScreenConnect partners and are actively investigating," ConnectWise told BleepingComputer.
"As a precaution, partners should avoid opening interactive ScreenConnect sessions to suspected compromised devices and use separate security tooling to investigate. Partners should also review account activity, revoke active sessions, reset credentials from a trusted device, and verify multifactor authentication."
The company said it would provide further information and guidance through the ConnectWise Trust Center.
Huntress has not yet determined how the attackers are gaining access to affected MSP environments, but says their current telemetry points to compromised credentials and hijacked MSP support sessions.
Huntress also warned that sequential identifiers used by the attackers suggest additional MSPs may have been previously compromised.
“Sequential attacker-assigned tags suggest other MSPs may have been compromised earlier, so ScreenConnect users should check their Run Command history even if they haven’t received alerts,” Huntress told BleepingComputer.
Huntress also shared indicators of compromise (IOCs) to help organizations identify malicious activity, including rogue ScreenConnect client IDs and infrastructure used by the attackers.
The indicators include:
-
Attacker relay:
185.99.255[.]28(hostname: screen) -
C2 domains:
newnewnew.gotdns[.]org,soxnewwork.homedns[.]org -
Possible additional C2:
cdn007-digitaldownloads[.]com -
Secondary C2:
sc.payproofkit[.]com(155.94.150[.]39, hostname: WIN-FB5CKHMU4E1) -
Stager:
hxxps://ns.mo7sen[.]dev/EadF.php?p=4 -
Rogue ScreenConnect client IDs:
2588ef5c15954b10,ed630cc2c873b091 -
Installer pattern:
/Bin/ScreenConnect.ClientSetup.msi?...&c=Exploited<N> -
Attacker name:
Addmin -
Files:
Panel-Lateral.ps1,runnew.cmd,ToolboxRelayUploader.exe,Run-Lateral-Full.bat
The researchers are urging MSPs to review their environments for signs of compromise and avoid initiating interactive ScreenConnect sessions with potentially infected endpoints.
BleepingComputer reached out to Huntress with additional questions about the attacks and will update the post if we receive a response.
Earlier malware activity linked to rogue ScreenConnect identifier
BleepingComputer found an earlier malicious batch script that references one of the rogue ScreenConnect client IDs listed by Huntress, suggesting that the ID was used in malicious activity months before the current attacks were disclosed.
The script, named SSA-2026-STATEMENT-15518787.bat [VirusTotal], appears to impersonate a Social Security Administration statement and was first uploaded to VirusTotal on July 25, 2026.
The batch file attempts to add Microsoft Defender exclusions and creates persistence through the Windows Startup folder and the Run registry key.
It then contacts amexsafekeyupdate.com to retrieve installation commands for two separate installers.
VirusTotal sandbox activity associated with the sample includes downloads of ScreenConnect MSI installers from cdn007-digitaldownloads[.]com and cyberrexdesign.screenconnect[.]com, with digitaldownloads[.]com listed by Huntress as a potential IOC.
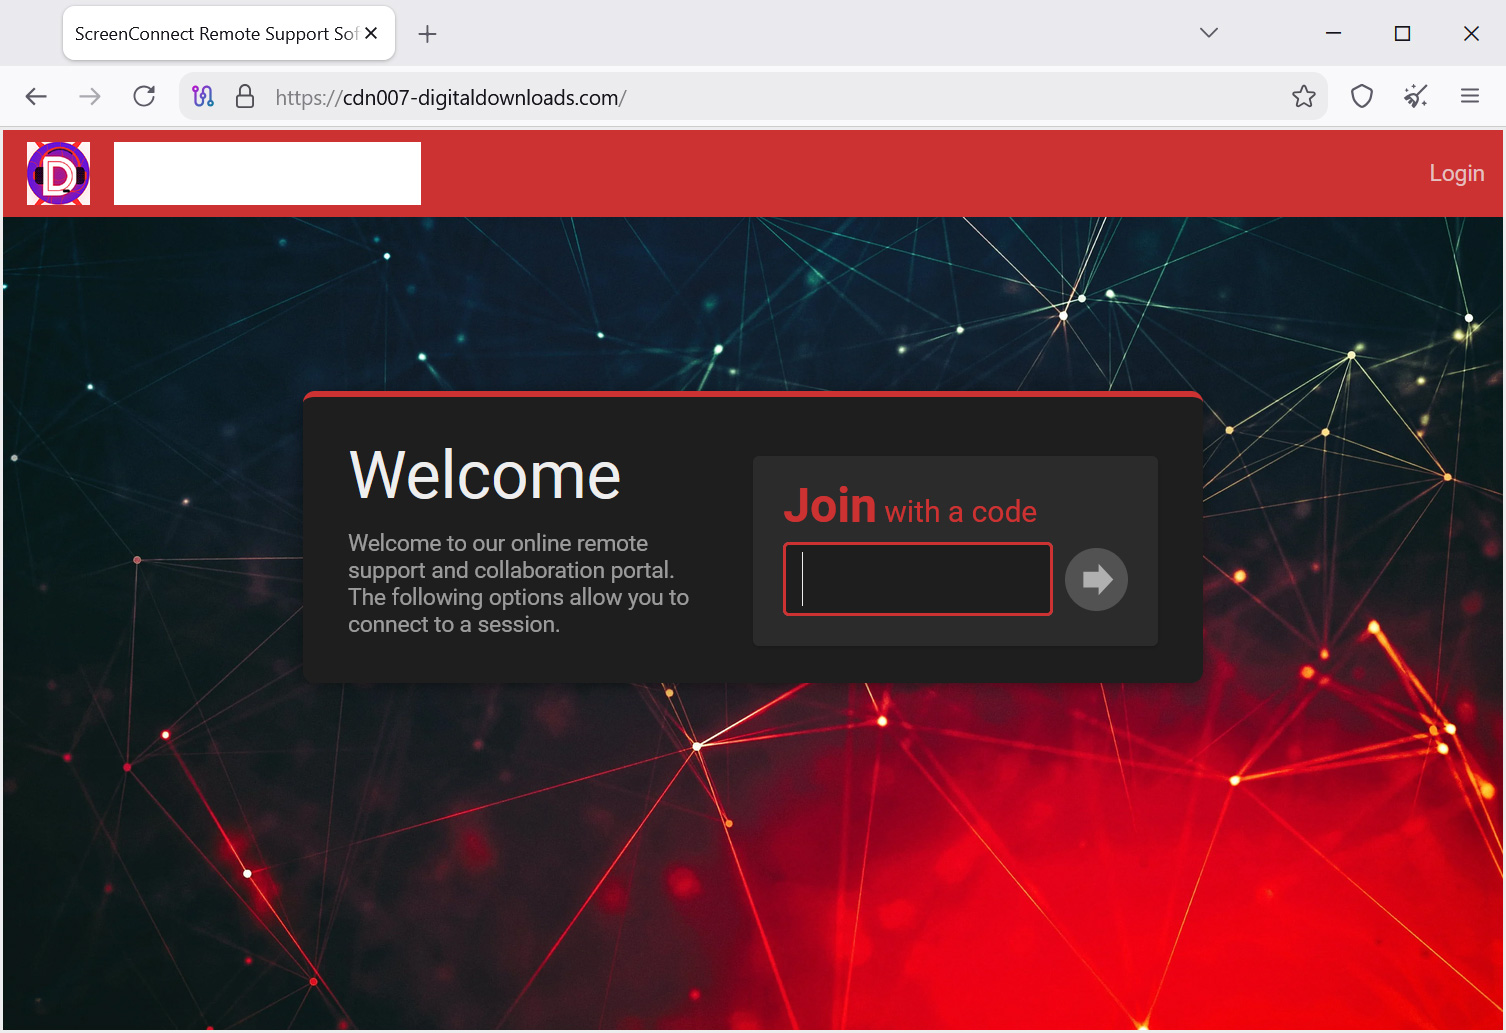
Source: BleepingComputer
After launching the second installer, the script uses PowerShell to search running processes and Windows services for ed630cc2c873b091, one of the rogue ScreenConnect client IDs identified by Huntress.
If the identifier is found, the script considers the installation successful and sends a notification to the attackers through Telegram.
The earlier script also appears designed for a different distribution campaign, with its Social Security-themed filename suggesting it may have been used in phishing attacks.
It remains unclear whether the July activity and the current MSP attacks are part of the same campaign.
Uncover email threats your existing defenses may miss.
Adaptive Security's AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what's getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.
Start your free email security scan.Originally published by BleepingComputer. Aggregated on AIWithGhost for educational purposes — full credit and traffic to the original publisher.